1. Install the Hub
This three-part quickstart runs Upbound Platform v3 on your laptop. Part one installs the Hub and the Console. Part two connects a second control plane. Part three creates a managed resource and watches it show up in the Hub.
This process takes up to 20 minutes and runs on local kind clusters. At any point, you can cleanly uninstall everything you created.
What you're installing
Upbound Platform v3 brings your control planes and the products that work with them together in one place. Every product comes bundled in the Hub, the central home for your platform's products and data.
Connect any Kubernetes cluster to the Hub as a control plane, and the Hub collects every resource running on it. When the control plane runs Crossplane, the Hub also shows the APIs it serves and the packages it installs. It doesn't matter how you run Crossplane: on a cluster with UXP, Upbound's official Crossplane distribution, or as a control plane in Upbound Spaces. Either way, you see everything in the Hub's Console, side by side.
By the end of this quickstart, you have a Hub running on your laptop, a second control plane connected to it, and a resource you created, visible in the Hub.
Prerequisites
Before you begin, make sure you have:
kindkubectlhelmversionv3.8.0or later- optionally, the up CLI, to install UXP with it instead of Helm.
The latest version of the Hub is free to try from November 4, 2026 to February 1, 2027.
Create a cluster
The Hub runs on a Kubernetes cluster. Create a local one with kind.
Demo mode publishes the Hub gateway on node port 30443. kind runs your node as
a container, so map that port to 8443 on your machine when you create the
cluster.
kind create cluster --name hub-quickstart --config - <<'EOF'
kind: Cluster
apiVersion: kind.x-k8s.io/v1alpha4
name: hub-quickstart
nodes:
  - role: control-plane
    extraPortMappings:
      - containerPort: 30443
        hostPort: 8443
        protocol: TCP
EOF
Install the Hub
Install the Hub chart in demo mode. Demo mode bundles the supporting infrastructure that you need to bring when you go to production.
helm upgrade --install hub oci://xpkg.upbound.io/upbound/hub \
--namespace hub --create-namespace \
--version 1.2.0 \
--set global.demo.enabled=true \
--wait --timeout 10m
What the chart installs
Every Hub install creates four components in the hub namespace:
| Component | What it does |
|---|---|
hub-core | Serves the APIs for realms, access control, control planes and Spaces, and Insights. Issues the registration tokens connectors register with, and stores the resources they sync. |
hub-auth | Issues Hub tokens: Console login, token exchange, and the keys hub-core verifies tokens with |
hub-connector | Registers this cluster's control planes with the Hub |
hub-webui | The Console |
global.demo.enabled=true adds the rest of the stack:
| Component | What it does | In a production install |
|---|---|---|
| Keycloak | Identity provider behind Console login | Point the Hub at your own OIDC provider |
| PostgreSQL | Database for hub-core | Supply your own PostgreSQL instance |
| An endpoint secured with TLS | Publishes the Hub at hub.127.0.0.1.nip.io with a self-signed certificate | Use your own hostname, load balancer, and certificate |
| Demo users and their RBAC bindings | Lets you sign in and compare permission levels | Map your own users and groups |
The demo PostgreSQL writes to an emptyDir, so its pod losing its node loses
your Hub data. Demo mode is for trying the Hub out. Don't run it in production.
Check out Insights in the Console
The port mapping from the kind create cluster step already publishes the
Console. Open your browser to the
Hub dashboard.
The pages under Explore are Insights, the part of the Hub that aggregates resources from every connected control plane and serves them through one API. The rest of this quickstart uses Insights to watch each control plane and resource you add.
This demo uses a self-signed certificate, so your browser warns you the site isn't secure. In Firefox, select Advanced then Accept the Risk and Continue. Chrome and Safari put the same option behind Advanced. Expect the warning: the demo runs on your own machine with a certificate no authority signed. A real Hub install uses a certificate you supply.
Sign in as admin with the password admin.
The dashboard counts the control planes, resources, and definitions the Hub sees:
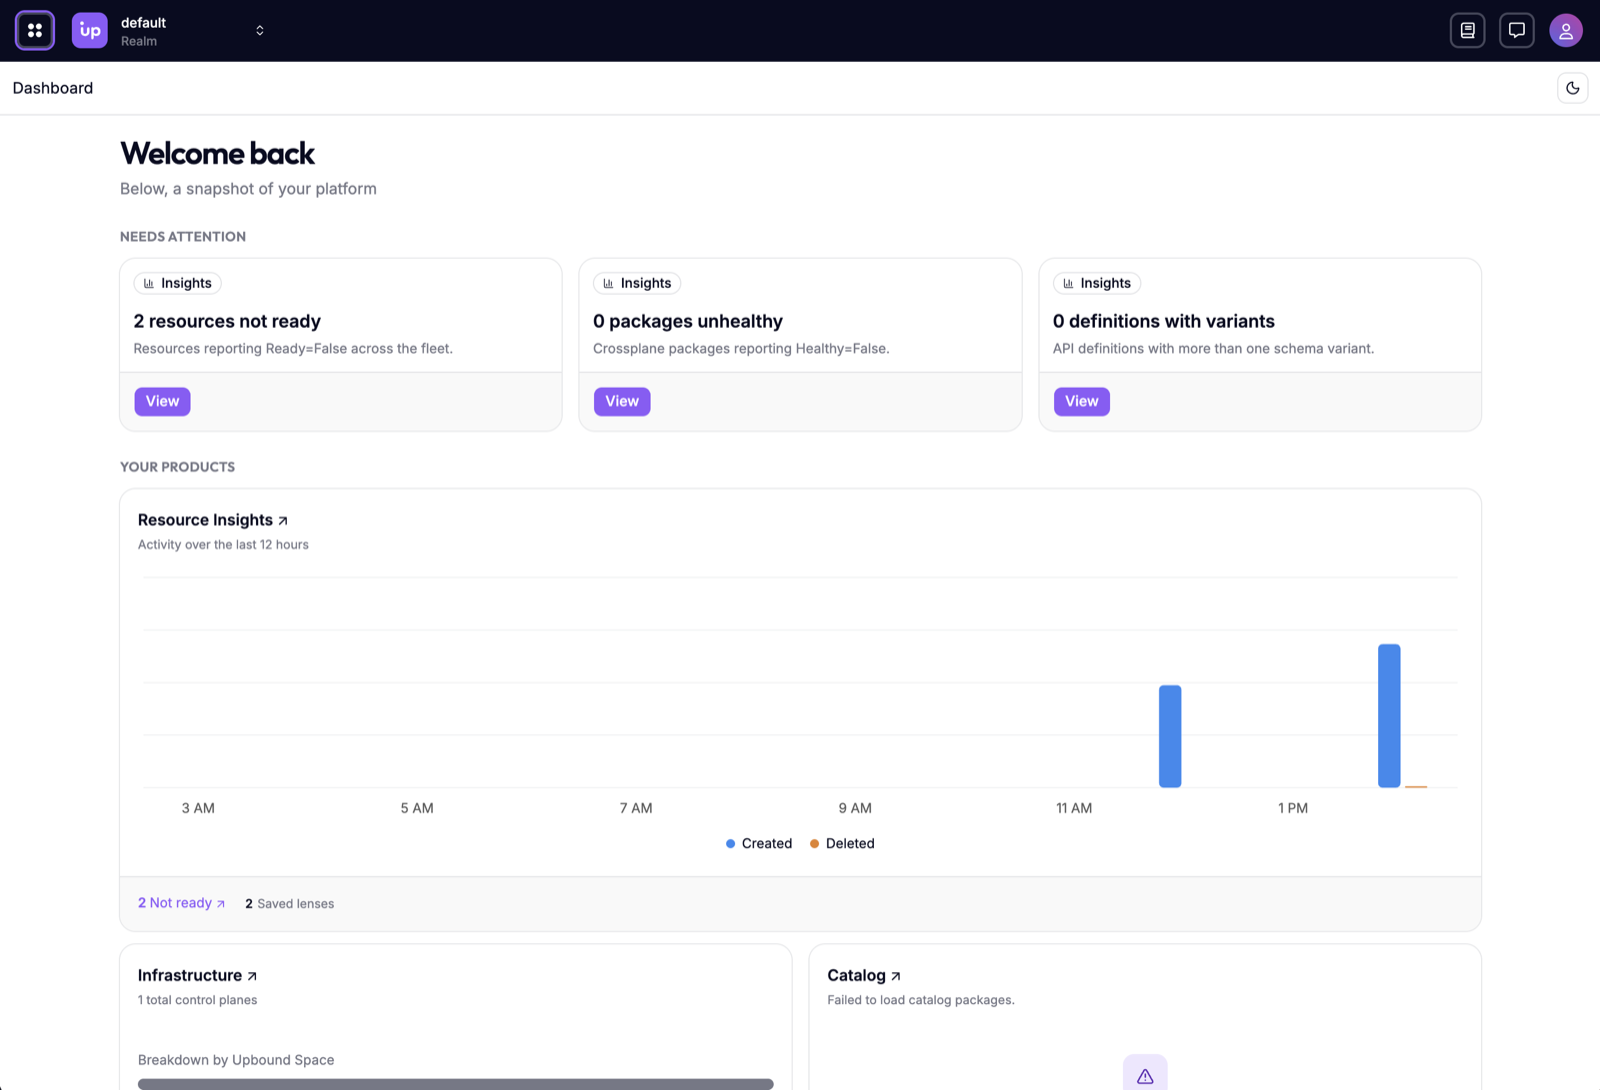
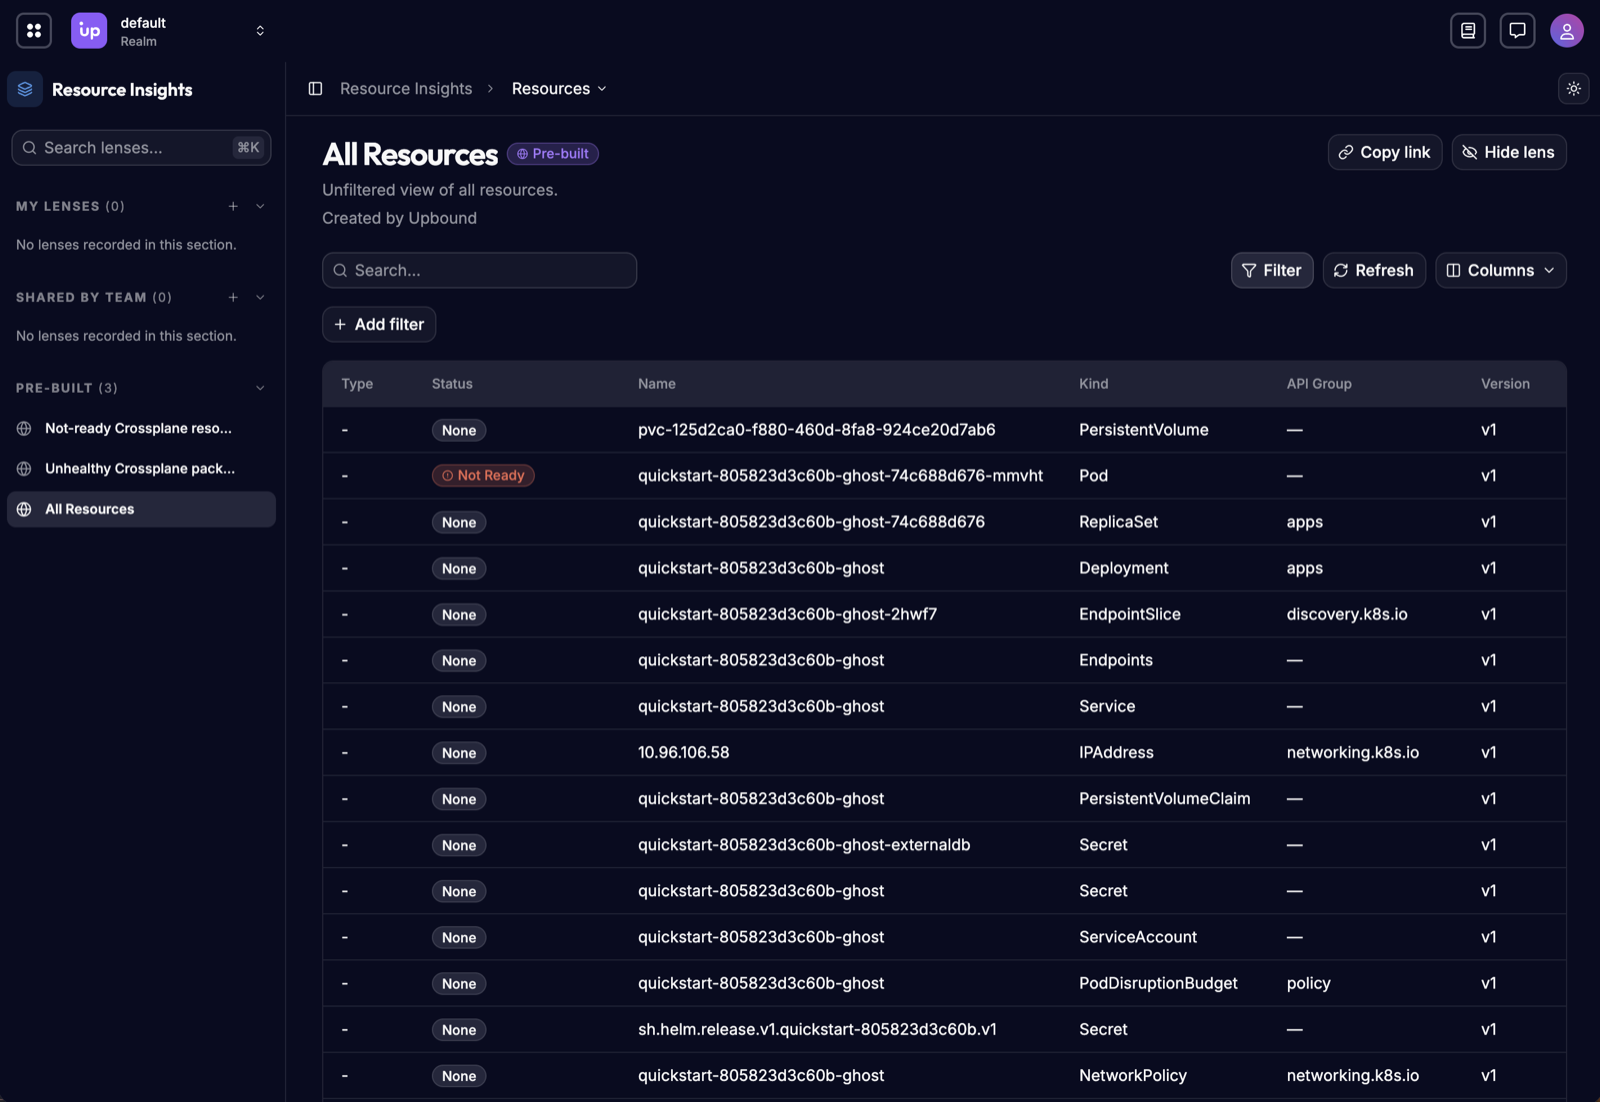
The resources page lists every resource the Hub sees. Because the Hub's own cluster is a connected control plane, the list includes the components that run the Hub. Filter or search by name to see one of them, like Keycloak, as the Deployment, Pod, Service, and ConfigMap behind it:
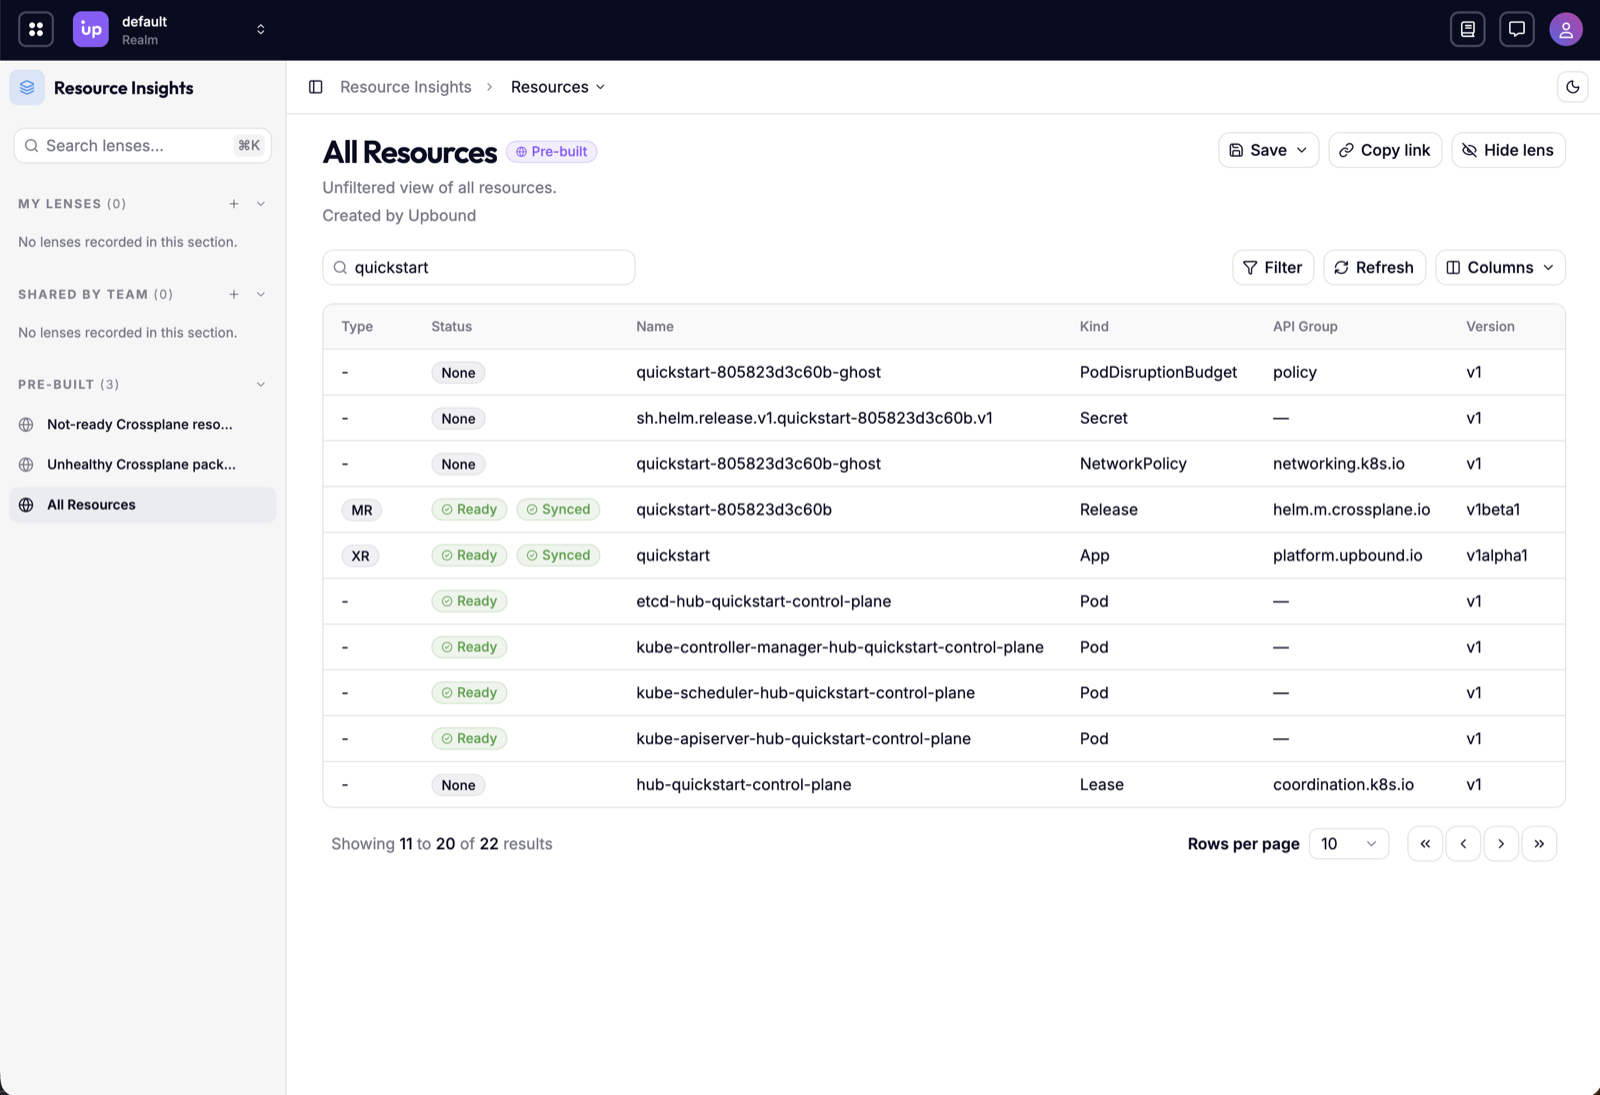
The definitions page lists every API kind across the connected control planes. See Definitions for what Insights correlates there:
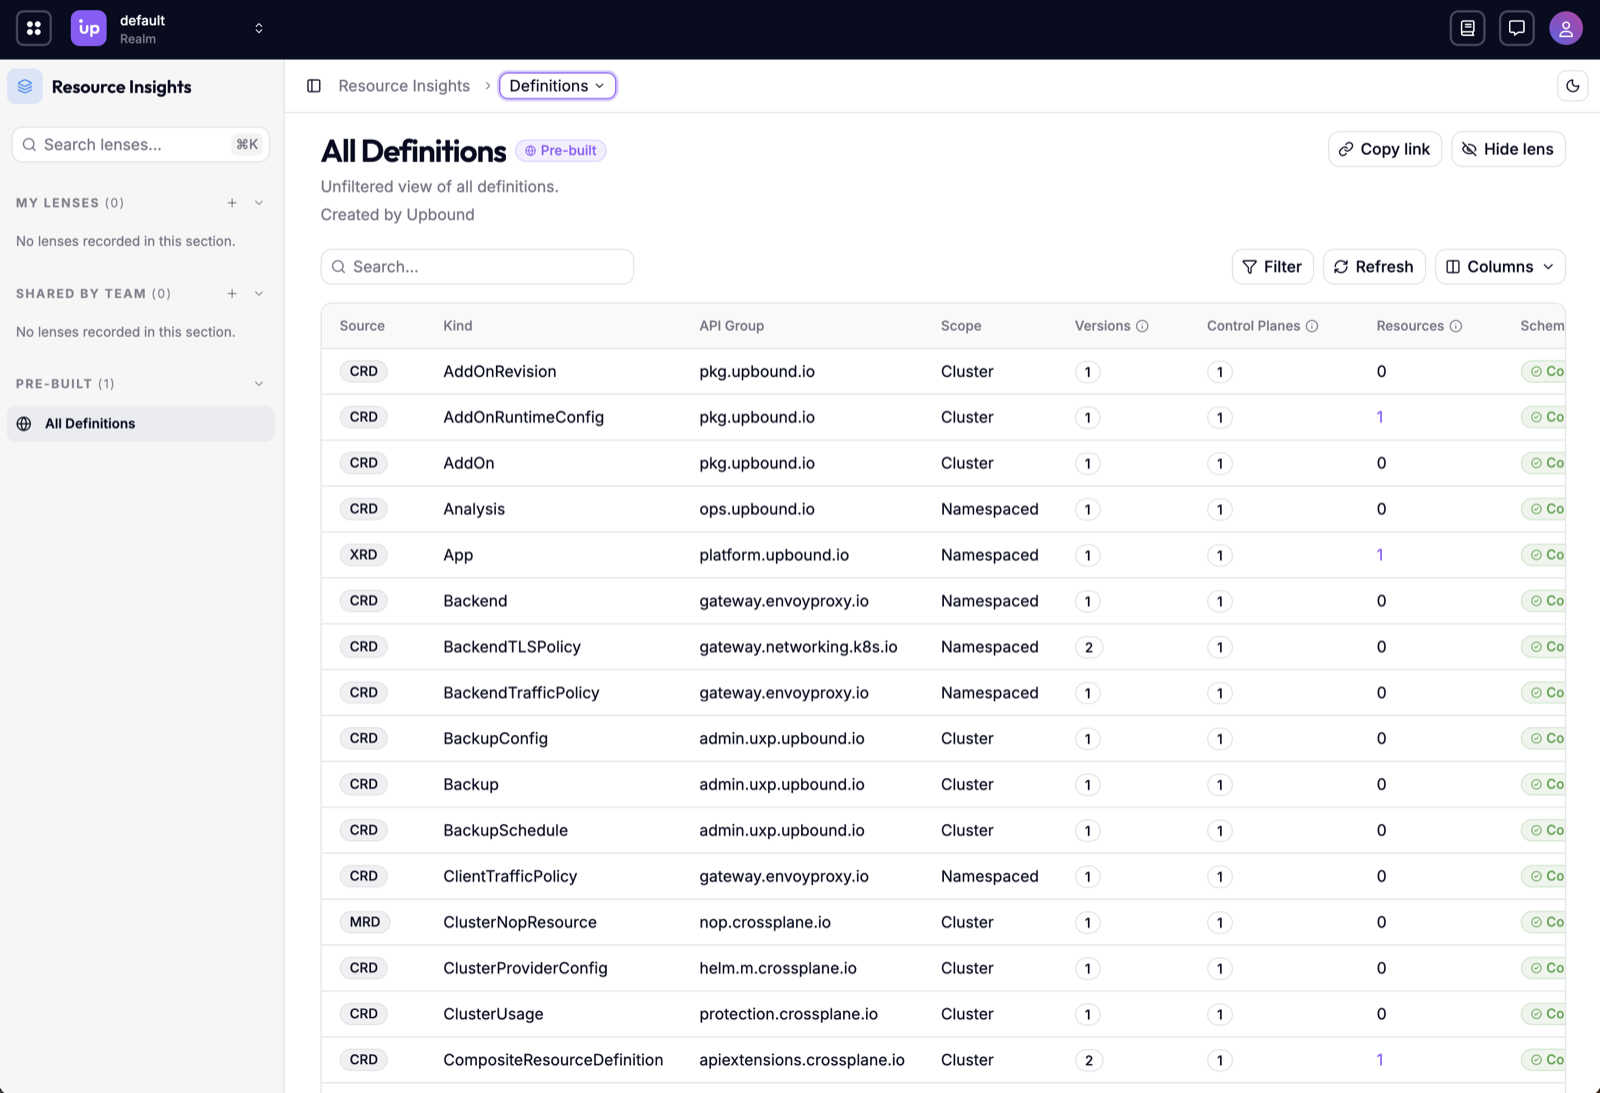
Demo mode also creates five other users, each with the password password, so
you can see how the Console changes with permission level:
| Username | Group |
|---|---|
admin | admin |
editor-alice, editor-bob | editor |
viewer-charlie, viewer-diana, viewer-eve | viewer |
Next steps
- Part two to connect a second control plane to the Hub.
- Insights for everything the Explore pages can do.
- Builders workshop for real cloud resources.
- Explore the Hub for the centralized management installation.
If you're stopping here, follow Clean up to delete what you created.